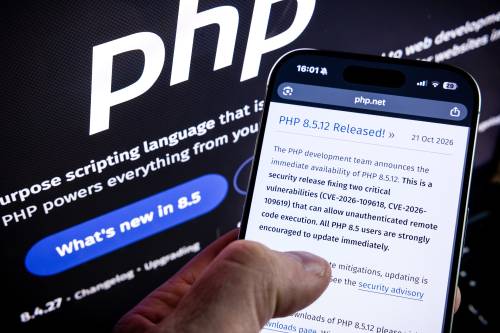
A long-delayed patch for a newly exposed vulnerability in the PHP programming language resulted from a “structural failure”, according to the PHP Foundation. The organization behind the language revealed that developers suspected the flaw could be exploited as early as 2024. However, progress stalled repeatedly due to internal disagreements within the PHP security team over the correct solution, compounded by a small pool of developers with the required expertise. The foundation acknowledged that poor decision-making processes and a lack of resources caused the prolonged delay. In response, the security team has updated its workflow, replacing unanimous decision-making with majority voting to resolve future deadlocks faster.
Information leak and impact on Dutch infrastructure
Cybersecurity firms including OpenAI, Calif, and Wiz highlighted the severity of the flaw earlier this year. Developers originally planned to disclose the vulnerability broadly only after releasing the official patch. However, premature leaks on social media, an accidental early video release by Calif, and an embargo breach by Chainguard exposed technical details before organizations could secure their systems. The vulnerability triggered widespread disruption across the Netherlands, forcing major institutions like Schiphol Airport to disable customer-facing applications and causing preventative system shutdowns at retail giants like Ahold Delhaize. To fix the issue, the PHP Foundation has deployed emergency security patches, while organizations worldwide update their servers, overhaul internal security protocols, and apply strict access controls to prevent potential exploits.
@ anp | NEWS BRAINPORT